Security
December 3, 2018
Today the IT world is very focused on high performance, high throughput interfaces.
In this situation, it is common to find REST and gRPC API, given their performances compared to the other solutions.
Sometimes, though, we still encounter old API written with older techniques or new API that for some reasons have been developed with outdated technologies.
One of those cases that I’ve encountered a few times over the last few months is SOAP.
Read More 
November 18, 2018
There are some pieces that you need to put in every microservice you write.
Those are for instance logging, error handling, authentication.
Over the last year, I found myself writing over and over CORS headers.
This requirement brought me to think that I should have used a Negroni middleware since we are already using Negroni for other middlewares.
I started looking online for an already written one, and I found a bunch, but I was not happy with what I found, so I decided to write my own.
Read More 
August 31, 2018
Lately, I found myself to work on an application that was communicating via SOAP with a server.
My goal was to understand how this application worked with the SOAP server to emulate its behavior.
Even if I had access to the source code of the application, I thought it would have been easier, faster and more fun to do the work without actually reading the code.
It’s important to note that actually, the application is fairly small and self-contained. Otherwise, I would have probably taken a different approach.
Read More 
July 13, 2018
If you have ever used Docker or any other Linux OCI container system, you inevitably have incurred in the following error:
x509: failed to load system roots and no roots provided
This message is remembering you that you forgot to provide Root Certificate Authorities to your application.
There are two different ways to solve this:
- mount the /etc/ssl/certs folder from the machine where the container is running
- bundling the root CAs in your image
As you may imagine from the title, I believe that the second option is by far better than the first one.
Read More 
June 27, 2018
Lately, all website are urging their users to enable second-factors.
The push for multi-factor logins is a good thing from my point of view, since the people are putting more and more details of their life online and is a good thing that companies start to understand the security implication of this and are trying to teach their users good security practices.
The real problem is what is defined as second-factor.
The possible factors are three:
Read More 
December 21, 2017
A few months ago, I posted how to create a PKI in Go.
Today I’d like to add share a useful function (at least from my point of view) that I found myself to write.
The problem arose when I had a function that required as input a *pem.Block of the public key, but all I had was the PEM file containing, as you can imagine:
- the Private Key
- the Public Key
- the CA Public Key
I think this is a typical situation, and for this, I’d like to share a function I wrote to extract it.
I know that it’s probably not perfect, but it could be a good starting point for many of you, and if you have suggestions, please leave a comment down below or send me an email, and I’ll update the post!
Read More 
November 3, 2017
Authentication factors
One of the common way to create more secure authentication in systems is adding more “factors”, creating in this way a Multi-Factor Authentication (MFA).
The idea behind MFA is that there are many different ways to authenticate a user, and those can be split in different “categories” based on the kind of challenge we require.
Generally speaking, it’s common to divide the authentication methods in mainly three categories:
Read More 
June 5, 2017
Lately I have been programming quite a bit and - for the first time - I have used Golang doing so.
Go is a very nice language and really helped me with the development.
One of the reasons why I have enjoyed this much Go is the standard library, which is amazing.
I would like to share today the easiness of creating a basic Certificate Authority and signed certificates in Go.
Read More 
April 13, 2016
Yesterday, Let’s Encrypt moved from beta to GA.
During the beta phase, which started last September, more than 1.7 million certificates were issued.
I think this is a crucial step for the project and overall for the Internet as well.
Until now, the only way to obtain a valid TLS certificate was to pay a CA.
This artificial constraint made no sense since the CAs were forcing users to buy an insurance policy that made no sense (and often, it was completely worthless).
Read More 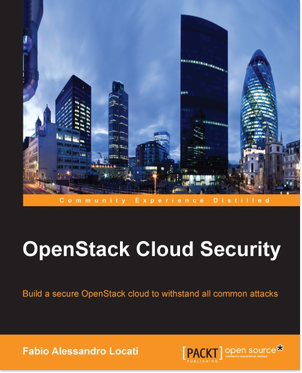
Published on July 28, 2015
Authored by Fabio Alessandro Locati
Published by Packt Publishing Limited
OpenStack is a system that controls large pools of computing and networking resources, along with cloud storage, allowing its users to provision resources through a user-friendly interface.
OpenStack helps developers with features such as rolling upgrades, federated identity, and software reliability.
You will begin with basic security policies, such as MAC, MLS, and MCS, and explore the structure of OpenStack and virtual networks with Neutron.
Next, you will configure secure communications on the OpenStack API with HTTP connections.
You will also learn how to set OpenStack Keystone and OpenStack Horizon and gain a deeper understanding of the similarities/differences between OpenStack Cinder and OpenStack Swift.
Read More
Buy it on Packt
Buy it on Amazon  (Fabio Alessandro Locati|Fale)'s blog